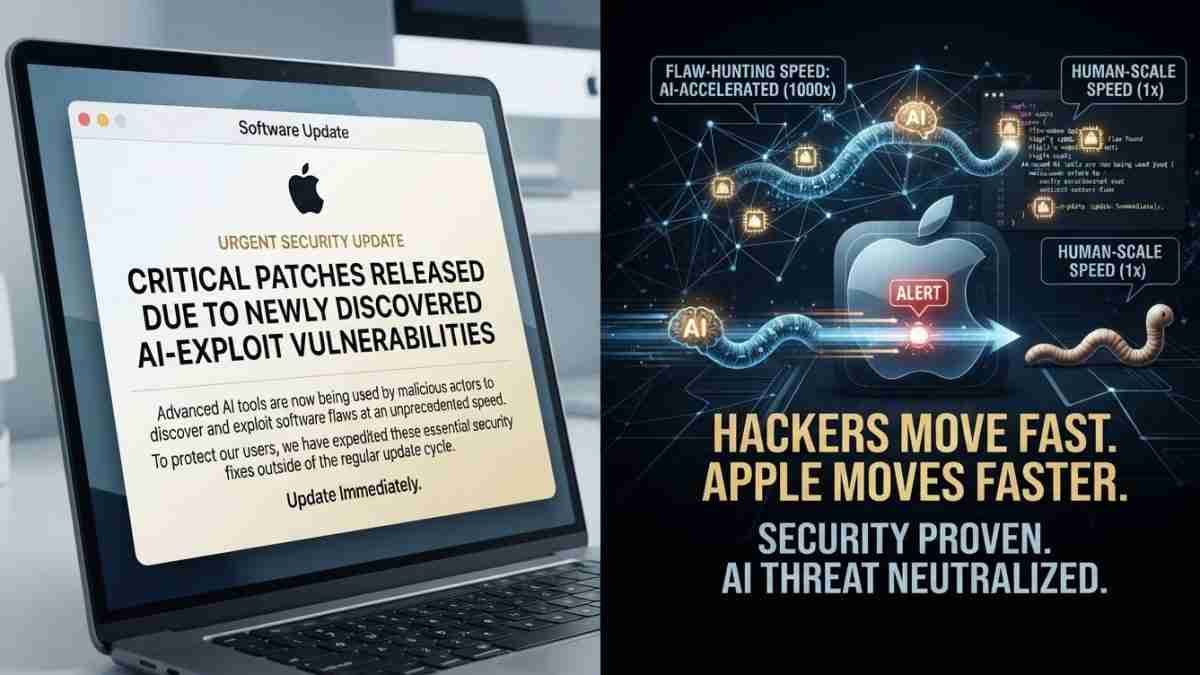
CUPERTINO, Calif., July 11 (San Francisco News Online) — Apple has pushed security updates for iPhone, iPad and Mac ahead of its normal software cycle, saying the change is meant to close the gap between when a flaw is found and when users get the fix.
The company told Reuters that it is shortening that window because artificial intelligence can help attackers build malicious hacking tools faster. Apple also said it had no evidence that the newly patched flaws had been exploited.
What changed
Apple usually folds security fixes into broader software releases. Reuters reported that this time, Apple broke from that pattern and released updates early, before the wider iOS 26.6, iPadOS 26.6 and macOS Tahoe 26.6 rollout.
The June 29 release included iOS 26.5.2, iPadOS 26.5.2 and macOS Tahoe 26.5.2, according to Apple’s release information as summarized by Reuters, Fox News and Quartz.
That matters because the earlier a fix is shipped, the less time attackers have to study a public bug and turn it into an attack.
What the update fixed
Apple’s security notes, as summarized by Fox News and Quartz, covered flaws in several core parts of its software:
- the kernel, which is the core part of an operating system that manages memory and other basic tasks
- WebKit, the engine behind Safari and many other web features
- WebRTC, which handles real-time audio and video in web apps
- libxslt
- IOGPUFamily, a graphics component
Fox News reported that the bugs could have led to app crashes, kernel memory corruption, leaks of sensitive kernel state, or sandbox escapes. In simple terms, those kinds of flaws can sometimes let a bad app do more than it should.
Quartz reported that some of the discoveries were credited to researchers using AI tools, including work associated with Anthropic’s Claude and OpenAI Codex Security. That does not mean AI created the bugs; it suggests AI is helping some researchers and attackers move faster when they look for weaknesses.
Why AI changes the security race
Apple’s explanation lines up with a wider concern in cybersecurity: AI can speed up both bug hunting and exploit writing.
Reuters reported that Apple said the time between public disclosure and customers getting protection can matter more now because AI can accelerate the development of harmful tools.
Quartz reported that the Five Eyes intelligence alliance has warned that frontier AI could fundamentally change offensive and defensive cyber capabilities and shorten the time between finding a flaw and weaponizing it.
That is the core issue behind Apple’s move. Security teams have long faced a race to patch before criminals act. AI may be making that race shorter.
Is this a sign Apple found an active attack?
Not based on what Apple has said so far. Reuters reported that Apple said it had no evidence the patched vulnerabilities had been exploited.
That is an important distinction. A company can release an urgent update either because it sees active abuse or because it thinks the risk is high enough to act before abuse is confirmed. In this case, Apple pointed to the second reason.
What users should understand
For users, the practical message is straightforward: install the update when it is offered.
The release covered supported iPhones, iPads and Macs, and Quartz reported that iPhone 11 and later were included, along with several iPad model lines.
The larger lesson is about timing. Apple is not saying AI has already taken over hacking. It is saying the tools available to attackers are getting faster, so security fixes may need to move faster too.
That turns a routine software update into a sign of where cybersecurity is headed: less time to react, and more pressure to patch early.